

What an Email Header Actually Reveals, and What It Does Not
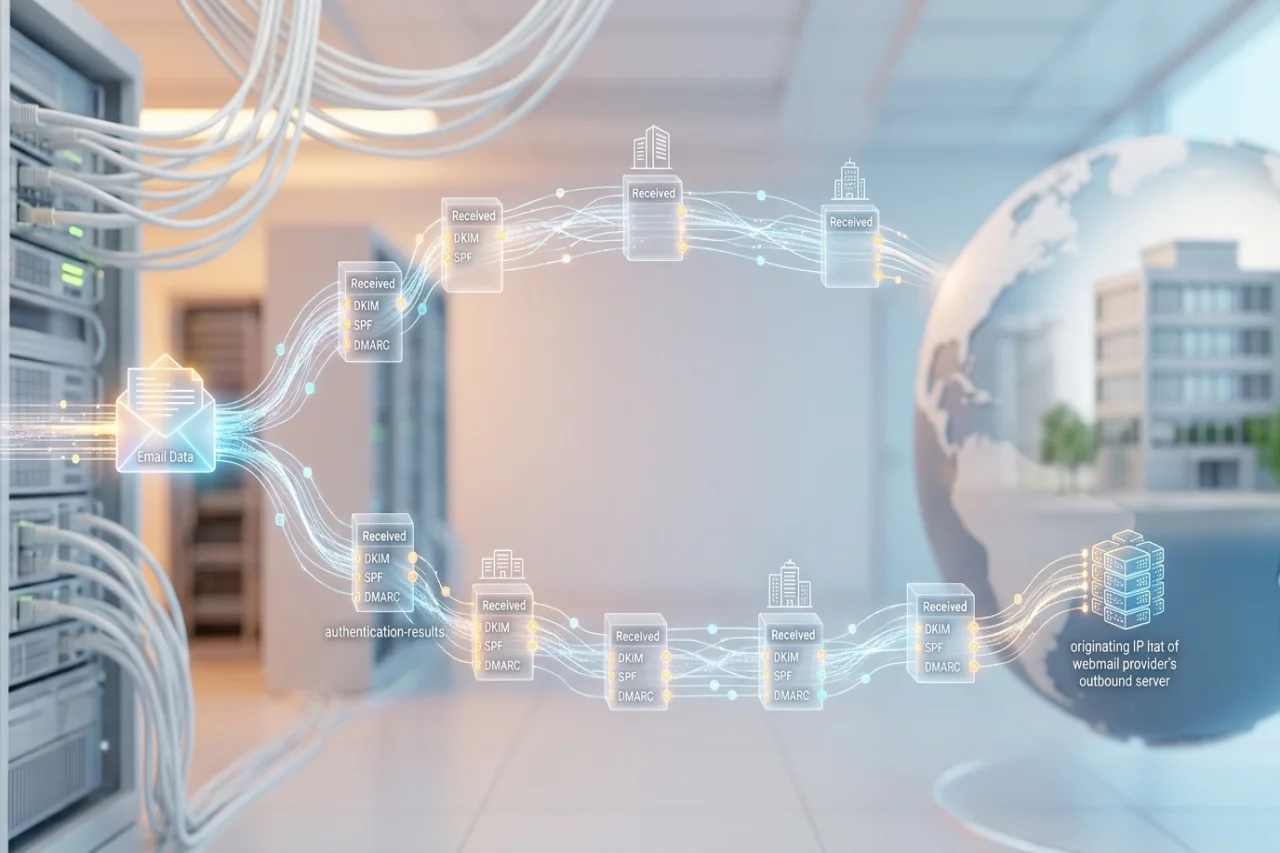
The header tells you which servers handled a message, not where the sender was sitting.
Most people treat an email as its body text. The message is what you read, and everything else is plumbing.
The plumbing is more interesting. Every message carries a header block that records the path it took, the servers that handled it, the authentication results, and, depending on how it was sent, the sender's IP address. If you have ever looked up an address to work out where a connection came from, the same curiosity applies here, and the answers are more nuanced than people assume.
Reading the trail
Open any message in your mail client and look for the option to show the original or the source. You will get a block of lines above the content.
The ones worth understanding:
- Received lines: These are added by each server that handles the message, newest at the top. Read them from the bottom up, and you have the route the message traveled. The lowest one is closest to the origin.
- Return-Path: This is where bounces go. It is not always the same as the address shown in the From field, which is the first thing to know if you are trying to work out whether a message is what it claims to be.
- Authentication-Results: This is the receiving server’s verdict on SPF, DKIM and DMARC. This is the part that actually matters for judging legitimacy, and it is the part almost nobody looks at.
- X-headers: These are non-standard additions from mail software, spam filters and marketing platforms. They vary wildly and often reveal which tooling the sender uses.
The IP question
The common assumption is that a header always exposes the sender’s home address. It usually does not.
If someone sends through a webmail interface, the originating IP recorded is generally the provider’s outbound server, not the device that composed the message. Major providers stopped including the client IP years ago. What you see is infrastructure.
Mail sent through a desktop client, a self-hosted server or an application can be different, and in those cases an originating address may be present. Geolocating it tells you roughly where that server sits, which is not necessarily where the person sits. A lookup returning a data center in one country says nothing about the human involved, and treating the two as equivalent is how people reach confident wrong conclusions about who sent something.
For a practical sense of what identifying information leaks in ordinary use and what to do about it, the Cybersecurity and Infrastructure Security Agency publishes guidance aimed at non-specialists.
Why the From field proves nothing on its own
Here is the part that surprises people who have not looked at mail protocols before: the From address is written by the sender. It is a text field. Nothing about the protocol requires it to be true.
That is why the three authentication mechanisms exist.
- SPF: Publishes, in DNS, which servers may send mail for a domain. The receiving server checks whether the message arrived from one of them.
- DKIM: Attaches a cryptographic signature that the receiver validates against a public key in the domain’s DNS, confirming the message was not altered and genuinely originated from the domain.
- DMARC: Tells receivers what to do when the first two fail, and lets the domain owner collect reports on mail sent in their name.
When you are assessing a suspicious message, the Authentication-Results line tells you more in one glance than any amount of IP geolocation. A message that fails DMARC while claiming to come from a bank is answering your question already.
Which matters if you send mail yourself
The same mechanics run in reverse when you are the sender, and this is where a free address quietly costs you something.
Sending from a free provider means your messages inherit that provider’s shared reputation and carry its domain in the From field. You have no control over the authentication records and no ability to signal that a message is from your organization rather than from anyone else with an account there.
Sending from your own domain changes that. You publish your own SPF, DKIM, and DMARC records; you control who is authorized to send in your name, and the receiving server can verify the claim. A professional email account on a domain you own is the practical route to that for a small team, without running a mail server.
The reputational effect is real but secondary. The technical effect is that your mail is verifiable, and a verifiable message is one that arrives.
A short checklist for suspicious mail
- Read the Authentication-Results line before anything else
- Compare the From address with the Return-Path
- Read the Received chain from the bottom up and look for a break in the sequence
- Treat a geolocated IP as information about a server, not a person
- Check links by hovering rather than by trusting the display text
The takeaway
Headers are informative, but they are informative about infrastructure. They tell you which systems handled a message and whether the sending domain could prove its claim. They rarely tell you where a person was sitting.
If you want to be judged accurately in the other direction, the answer is the same: send from a domain you control, with the records published, so the verdict on your mail is based on evidence rather than guesswork.
Comments
Comments are available to signed-in users and are moderated to keep the discussion useful and respectful. Spam, automated submissions, and low-value promotional comments are removed. Outbound links may be approved when they are relevant and genuinely helpful to readers, but they are displayed as plain text rather than clickable hyperlinks.
No comments have been published yet.
Please sign in to submit a comment.