

How Websites Really Detect Proxies, Despite the IP Having a 0 Fraud Score
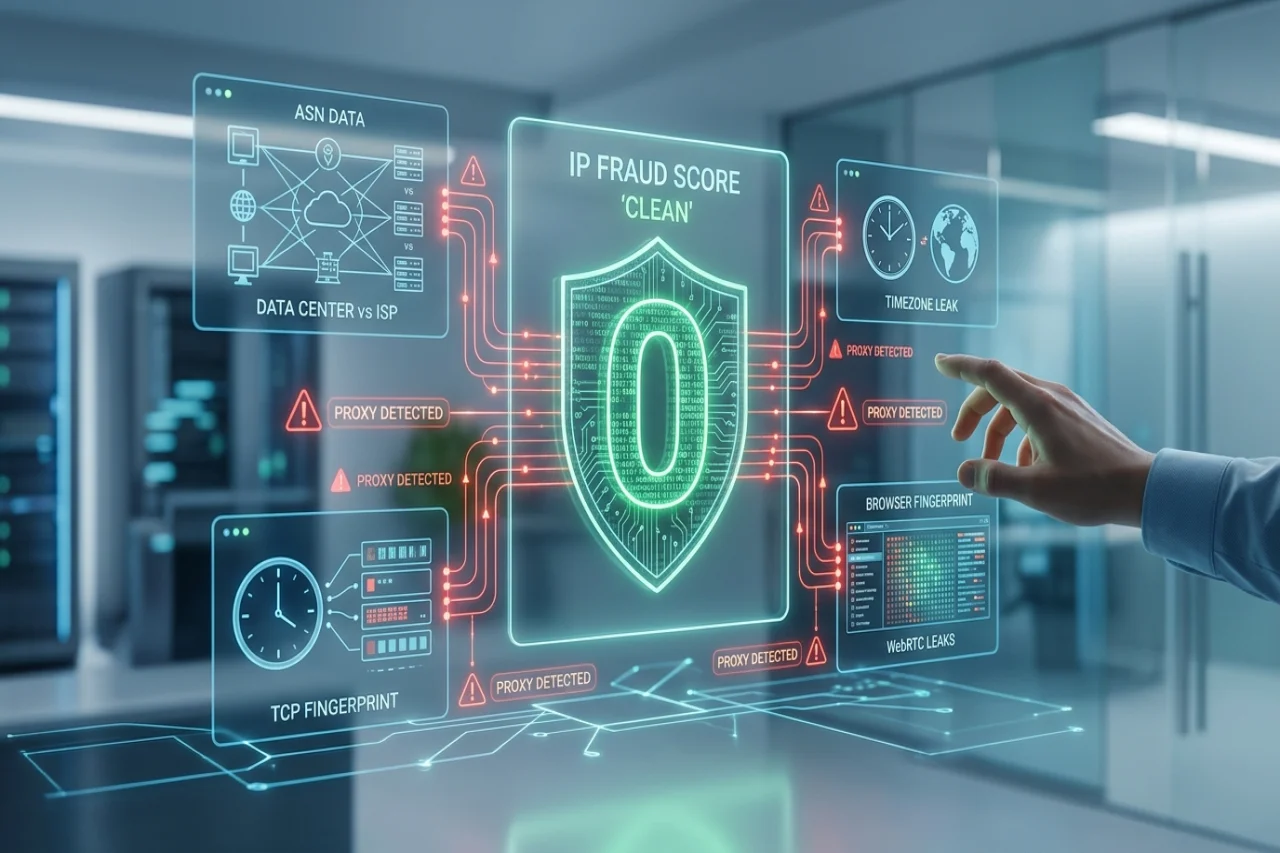
Did you buy a new proxy and have a 0 fraud score, and then get flagged by a website that you really, really care about? How do websites even check proxies? How do I check if a proxy is used? I bought a new proxy; it shows a 0 fraud score. I looked up the IP, and it says it was issued by an ISP. My favorite website required me to provide my phone number, showed a "proxy detected" message with a fingerprint checker, and now my account is locked on the second attempt to log in. I understand that a 0 fraud score is real. It really answers a question a lot of people probably do not even know exists. It means no one has recently reported abuse against that address, but it says nothing about the rest of the data, which a proxy detection system reads in the first second of the user's visit. Let's look at the rest of the data and figure out how to check it yourself in 10 minutes, and what type of proxy and browser are needed to solve the issue.
What does proxy fraud score mean?
What information is not available on proxy fraud score? IP fraud score is the assessment of IP reputation. The IP fraud score is an automated numerical rating that is given by services such as IPQualityScore and Scamalytics based on the number of reported cases of abuse, presence on block lists, presence of open proxy ports, or bots that may have been running on the IP address range. As per IPQualityScore documentation, an IP with a proxy score of 75 or above is suspicious. A proxy fraud score of 0 is the "cleanest" rating possible. The proxy fraud score does not know you. It does not know your browser, operating system, or what connection you are using. It is only rating the IP address, as you would rate someone's credit when you have never met them before. Businesses like banks, marketplaces, ad networks, or social media networks can meet you. IP fraud score is just one of the many different factors they consider. It is usually not the most important.
Check 1: who owns the IP
Every IP address is part of an autonomous system (AS). Every autonomous system (or ASN) is owned by someone (a home broadband provider, mobile provider, hosting company, or university). This is public information, and the first thing a site will check. If the IP address is from a data center hosting company, it can have a low fraud score, but it is likely to be detected during a single IP address lookup because it is owned by a hosting company. It is very unlikely that a real customer would use a hosting company to browse. The sites see this as a good indication of fraud.
You can see this for yourself. You can use this site's IP lookup tool and enter an address to view ISP information from each database. Some of the databases go further into information such as ISP, MOB for mobile, DCH for data center, and hosting. If different databases show different information about the same IP address, it can be helpful, as the sites will use one of the databases, but it is unknown which one.
Check 2: is your location the same as where you are?
While your location will be found by IP geolocation, there's another source of information that a webpage could use to find out where you are: your browser. To determine a visitor's time zone, a webpage only needs one line of JavaScript code. The Accept-Language header that your browser sends with each request includes the list of languages spoken by your browser. The WebRTC API could also reveal a website associated with your IP address that isn't passed through a proxy server, since WebRTC uses UDP, which a simple HTTP proxy can't intercept. Your DNS server could also be located in your home country.
When we put it all together, we see a classic case of a location mismatch: Your IP addresses you to Chicago. Your browser claims you're in Europe/Berlin and speaks German. Then WebRTC quietly tells them your real IP address in Hamburg. They are all fine on their own, but when we put it all together it's an important warning flag.
Check 3: "proxy detected" results from the TCP fingerprint
The TCP fingerprint is a tool used to tell whether a connection has been hidden using a proxy. Almost nobody knows about it.
Proxies allow you to hide the actual computer that you are using. So if you are using a proxy to connect to a website, the website only sees your proxy connection and not your actual computer connection. Operating systems send different TCP packets. For example, Windows has a time-to-live of 128, while Linux, Android, and macOS have a time-to-live of 64. Windows sends packets one way, without adding timestamps, while Linux sends them the other way, with timestamps. A passive tool called p0f can determine which operating system is being used from the first packet it receives, without ever having to connect to the computer. This is called TCP/IP stack fingerprinting, and was around in the late 90s.
Almost all proxies run Linux, so when you visit a website in a browser, it tells the website you are using Windows 11 with Chrome, but the first packet sent actually shows you are using Linux. This was pointed out on the BrowserLeaks TCP/IP stack page and by whoer.net, and it is why many people are seeing "proxy detected" results when there is nothing wrong with them.
Changing your IP address will not affect your TCP signature, and improving your fraud score will not affect your TCP signature. The TCP signature generally needs to be addressed at the proxy server level. Some proxy providers have started modifying TCP signatures on their exit servers to better align with the operating system and browser presented by the connection. For example, Proxya offers this functionality on certain ISP proxies and data center proxies, with support for configurations such as Windows 11, macOS, and Android with commonly used browsers. Tools such as Proxya's Anonymity Check can also be used to compare the operating system reported by the browser with characteristics observed from the connection, providing one example of how TCP signature consistency can be evaluated.
Check 4: browser fingerprinting
A website can fingerprint your browser even if you are using different IPs or TCP signatures. Canvas/WebGL renders, installed fonts, audio processor, screen size, no. of CPU cores. All of this is enough to uniquely identify a device. That's how they matched up accounts, even though they were not using the same clean IP. They were not using the same IP. They were using the same laptop.
There is an anti-detect browser solution, but each user has a profile; they use different but consistent devices. Unfortunately, there are few anti-detection browsers that can fool detection algorithms. Many anti-detection browsers trick the algorithm by faking the device using a JavaScript wrapper that emulates all browser functions. A website can download a fresh copy of a function from an empty iframe and compare it to the original to see if a wrapper was added. Anti-detect browsers based on Chromium itself will not allow it, as the values are in Chromium.
One example is Proxya Anty, an anti-detect browser that provides multiple browser profiles and can be used to evaluate several configuration factors at the same time. For example, it can obtain timezone, locale, and geolocation information from the proxy exit before the browser window opens and use the proxy relay for WebRTC traffic. It can also generate device profiles based on a fingerprint catalog and supports externally added proxies in addition to Proxya's own proxy services. This provides one example of how an anti-detect browser can coordinate browser and proxy settings within individual profiles.
Behavior
Even if your best proxy is used, it will still be flagged if it is being run as a script. If the user types 10 text logins one after the other, then immediately pastes the same text into all text boxes, using the same click sequence and pace on each login, the models will notice it. A proxy or browser won't make any difference.
Can residential proxies, ISP proxies, or datacenter proxies be detected?
Answer: Yes, but in a different way.
Datacenter proxies
- When you look up an IP, it will reveal the name of the hosting company.
- The same IP? Yes
- What goes wrong: Check 1 on strict sites
- Most suitable for: Bulk scraping, speed, and sites not filtering by ASN
Rotating residential proxies
- When you look up an IP, it will reveal your home ISP.
- The same IP? No
- It changes for every request (or every few minutes).
- What goes wrong: Logins (address constantly changes)
- Most suitable for: Scraping, price, and verification of ads
ISP (static residential) proxies
- When you look up an IP, it will reveal your home ISP.
- The same IP? Yes
- Same address for the whole term.
- What goes wrong: Rarely on the IP level, if you have a clean pool
- Most suitable for: Accounts, long-term use, and any site behind a login
Mobile proxies
- When you look up an IP, it will reveal your mobile carrier.
- The same IP? Rotates according to the carrier's schedule
- What goes wrong: Mostly price
- Most suitable for: Social apps if mobile is expected
None of the 4 types of proxies can be used for check 3 or check 4 separately. This is what people tend to ignore.
Have a static ISP address, a TCP signature that matches your operating system, and a browser profile that has timezone and language that matches the exit ip and you will have a perfect combination for account work. Residential proxies will still work for scraping thousands of pages, and cheap data center proxies are the way to go if your target will never look at ASNs. Residential for 2.40/gb, data center for 1.70, and ISP for 2.50/month per proxy. So you don't have to pay for what you don't need, and you can pick the one that best fits your target.
How to self-check to see if your IP is being detected in 10 minutes
The following are 6 things you should do before you start accusing your proxy:
- Check to see what your ASN and usage type are for your exit IP. It is very simple to check out: any IP that comes from a datacenter is considered a hosted IP, and it doesn't matter what the seller says.
- Ask to see your fraud score from 2 different companies. The companies gain access to various data sources.
- Check to see where the IP is coming from and what timezone it is in, then check where your browser is telling you that it is and what your first language is.
- Run a WebRTC leak test while your proxy is on. Any address other than your proxy should be a leak.
- Run a TCP fingerprint checker and check your user agent's OS to see if it is the same as your packets.
- If you are using multiple accounts, check to see if all your accounts have different canvas and WebGL hashes.
If everything above has passed and you're still getting flagged, check the account history and your behavior before getting other IPs.
The downsides
Each proxy type has limitations. ISP proxies are generally more expensive than data center proxies and may be available in fewer locations. Rotating residential proxies can provide broader geographic coverage, but their changing IP addresses may not be suitable for applications that require a consistent connection. TCP signature modification also depends on the infrastructure and locations supported by the individual provider, while residential proxy exits depend on the characteristics of the networks and devices through which traffic is routed.
Anti-detect browsers also involve tradeoffs. Some are open-source, while others use proprietary components that cannot be fully reviewed independently. For example, Proxya Anty uses a closed-source browser engine, although Proxya also provides MIT-licensed SDKs and an MCP server. Open-source alternatives include Camoufox and Donut Browser. Regardless of the tool selected, anti-detect browsers do not override a platform's terms of service, and users remain responsible for complying with the rules of the websites and services they access.
Conclusion
A low fraud score alone does not determine whether a proxy will be detected. Websites may consider several signals, including IP reputation and ownership, geolocation consistency, TCP characteristics, browser fingerprints, WebRTC behavior, and account activity. Reviewing these factors together provides a more complete picture of how a connection may appear to a website.
Different proxy types also have different strengths and limitations, so there is no single option that works equally well for every use case. Understanding how each detection signal works can help users troubleshoot connection issues, identify configuration mismatches, and choose an appropriate proxy setup while following the terms and requirements of the websites they access.
FAQ
FAQ
01Are residential proxies detectable?
Residential proxies can be detected: The residential IP is recognized as a home ISP, but other things such as the timezone, WebRTC leak, the TCP signature (which differs from the real operating system), and the browser fingerprint may be tested.
02If your proxy is 0 fraud score does that mean that it is undetectable?
A 0 fraud score does not mean your proxy is undetectable; it only means that your IP has no history of abuse in the service's database in the past. 0 fraud score means absolutely nothing to your browser, the signature of your OS in the browser, or your behavior.
03Do I need the anti-detect browser if I use ISP proxies?
No, you don't unless you have multiple accounts or the site is super strict on fingerprinting. You will likely only need 1 account for most websites with an ISP proxy and a regular browser. You will need different profiles, or the devices will connect the accounts, if you are using the same IPs for multiple accounts.
Comments
Comments are available to signed-in users and are moderated to keep the discussion useful and respectful. Spam, automated submissions, and low-value promotional comments are removed. Outbound links may be approved when they are relevant and genuinely helpful to readers, but they are displayed as plain text rather than clickable hyperlinks.
No comments have been published yet.
Please sign in to submit a comment.